Platform & AI
Cardiology Platform System Design
A cloud platform built for how cardiology groups work: many hospitals, office labs, testing entities and a full history of every change.
Cardiology Platform System Design is the cloud architecture under Unlimited Systems for cardiology groups. It holds several entities, such as the physician group and an imaging facility, in one database. Every charge carries its site and component, every change is recorded, and access is limited by role under HIPAA safeguards.
 6,500+ specialty providers
Platform System Design in a Cardiology Practice
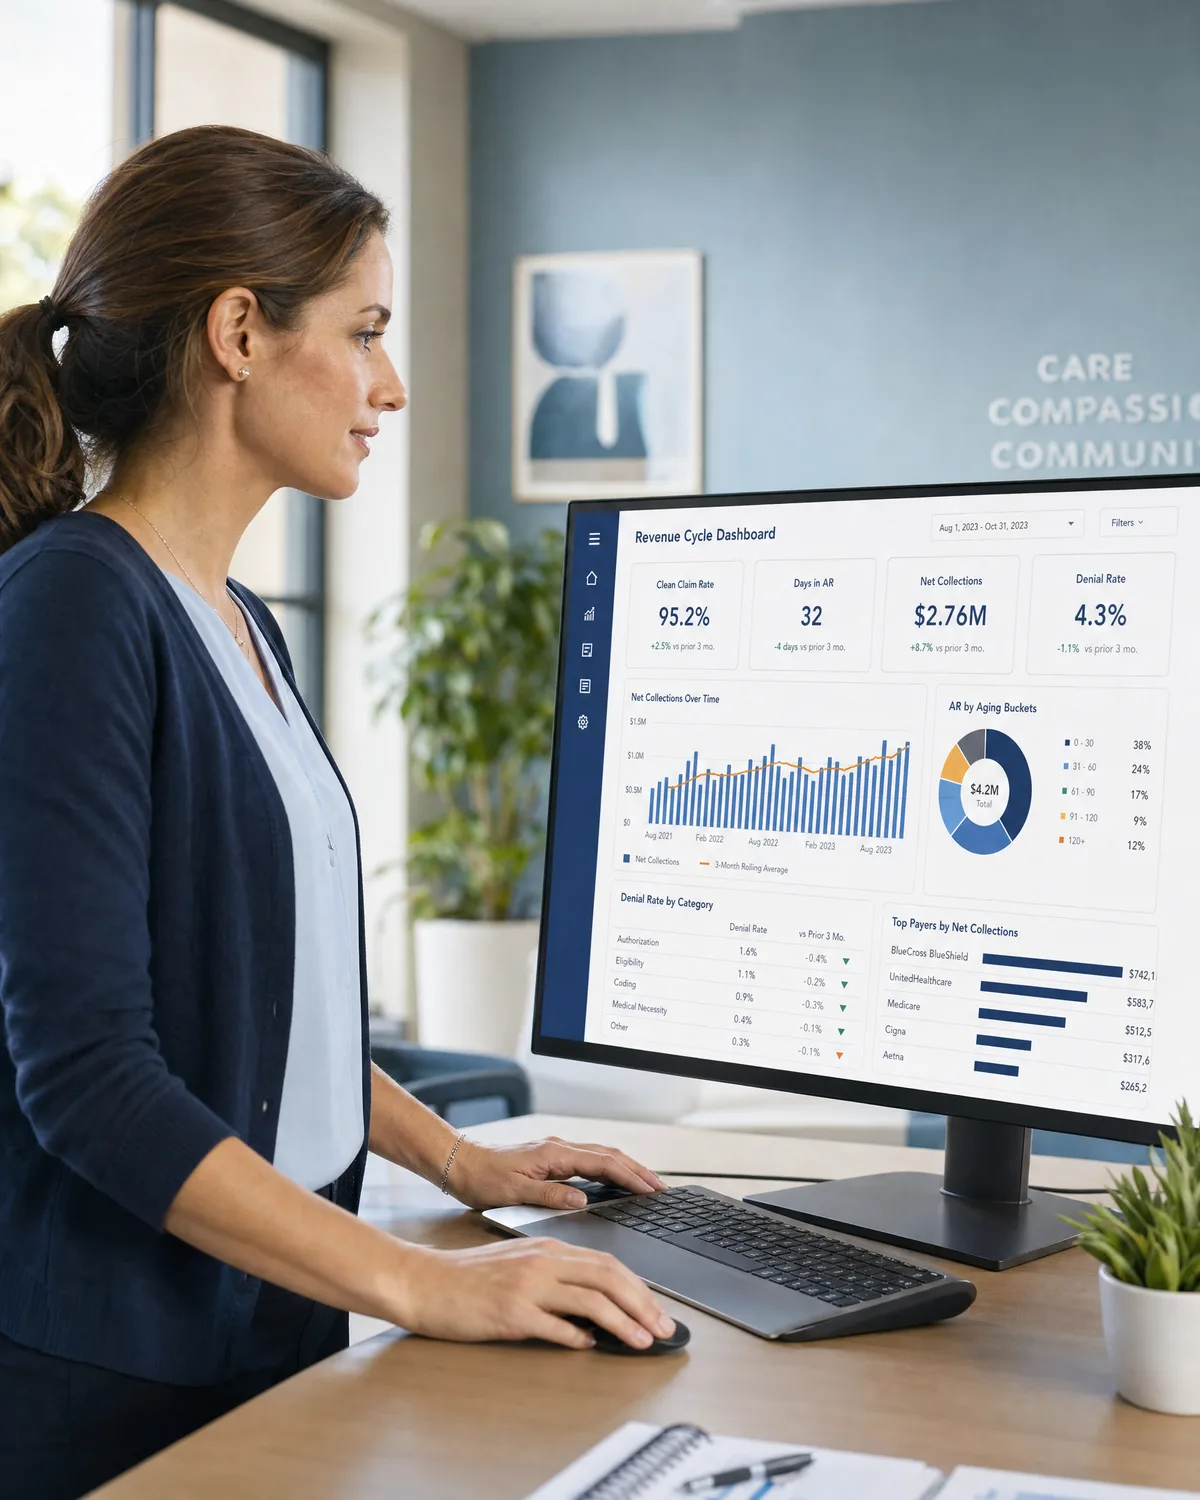
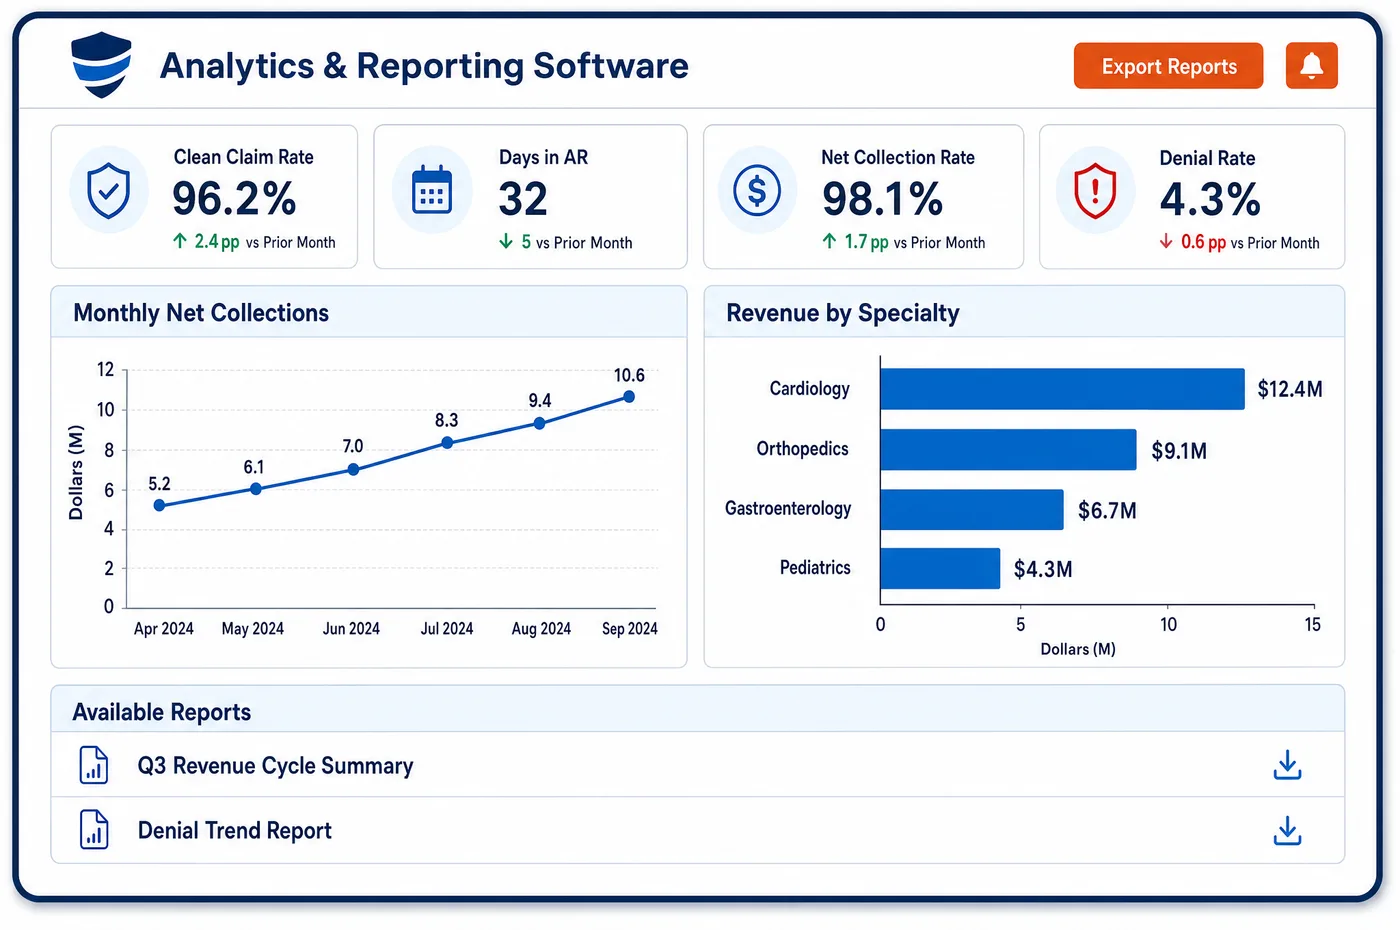
A cardiology group is rarely one simple practice. Its physicians may see patients in several offices, run echo and nuclear labs, read studies at many hospitals and staff a device clinic. Some groups bill testing through a separately enrolled facility or own part of an ASC. The platform system design starts by modeling that structure. Each entity has its own tax ID, NPIs, bank accounts and payer settings, inside one database. Each hospital where physicians read is set up as a site, so every charge knows where the work was done. Each charge carries its component, so office and hospital revenue never blur. The data model keeps every change rather than overwriting it, so an account's history can be audited line by line. Capacity scales on its own when hospital read batches or month-end volume spike. Staff at every site work in a browser on live data, and access follows each person's role, sites and entities.
Why Is Platform System Design Different in Cardiology?
Site of service is a design decision in cardiology, not a field to fill in later. The same CPT code pays differently in the office and at the hospital, and the group may read at a dozen hospitals. If the data model does not tie every charge to a site and component, no report, edit or posting rule can fix it downstream. The platform has to make site and component part of the charge from the start.
Entity structure is the second decision. A testing facility enrolled under 42 CFR 410.33 has its own Medicare enrollment and standards. An ASC has its own facility claims. CMS identifies ASM participants by the pairing of TIN and NPI, and MIPS subgroups split clinicians inside one TIN. A design with one practice per database forces staff into several systems. Holding each tax ID as its own entity on one platform keeps books apart while owners still see the whole group.
History and security finish the picture. Payers recoup, audits ask what was billed and why, and corrected reports change charges after the fact. A platform that overwrites records cannot answer those questions, so the design keeps every change. Patient data must be protected under the HIPAA Security Rule, with access limited to what each role needs. Those choices feed cardiology accounting and cardiology reporting, which depend on clean, complete data.
What Cardiology Platform System Design Handles
- Independent diagnostic testing facilities (42 CFR 410.33)
- A testing facility enrolled apart from the physician group is set up as its own entity, with its own enrollment, NPI and ledger. It still shares the patient record with the group. (42 CFR 410.33: Independent diagnostic testing facility)
- Type 1 and Type 2 NPIs
- Each physician's Type 1 NPI and each entity's Type 2 NPI are stored once. Claims for the group, the testing facility and any ASC use the right identifiers. (CMS National Plan and Provider Enumeration System (NPPES))
- TIN and NPI pairs for ASM and MIPS
- CMS identifies ASM participants by TIN and NPI, and MIPS subgroups split clinicians within a TIN. The data model keeps those pairings, so program reporting can be cut the same way. (CMS Innovation Center: Ambulatory Specialty Model (ASM))
- HIPAA Security Rule safeguards
- Administrative, physical and technical safeguards are built in: role-based access, audit logs, encryption and backups. Patient data is encrypted in transit and at rest. (45 CFR Part 164 Subpart C: HIPAA Security Standards)
- Minimum necessary access
- Users see only the sites, entities and records their roles need. A hospital read team sees its hospitals, and a lab manager sees the lab. (45 CFR Part 164 Subpart E: HIPAA Privacy of Individually Identifiable Health Information)
How Does Cardiology Platform System Design Work?
1. Model the entities
The physician group, any testing facility and any ASC are set up as entities with their own tax IDs, NPIs, banks and payer settings. Owners choose how they roll up.
2. Set up every site
Each office, lab and hospital where physicians work is a site. Charges carry the site and component from the moment they are created.
3. Keep every change
The database records each change instead of overwriting it. Any account's history can be shown for an audit or a payer question.
4. Control access
Roles decide which sites, entities and records each user can open. Each look at a record, and each edit, leaves an audit entry.
5. Scale and protect
The cloud platform scales with volume and keeps redundant offsite backups. New sites and entities are added on the same platform as the group grows.
Cardiology Platform System Design vs. Generic Software
| Area | Generic approach | Unlimited Systems |
|---|---|---|
| Entities | One database per tax ID. | Several entities in one database, each with its own books. |
| Site of service | A field staff may leave blank. | Part of every charge from creation. |
| History | Records overwritten on each edit. | Every change kept for audit. |
| Access | Everyone sees every site. | Roles limit users to their sites and records. |
| Hosting | Local servers at the main office. | HIPAA-compliant cloud with offsite backups. |
Who Uses It in a Cardiology Practice
- Physician owners: One view of the whole group, while the physician group, labs and any testing entity keep their own books.
- IT and security lead: Encryption, audit logs, role-based access and backups designed in, plus a business associate agreement that covers the platform.
- Operations director: New offices, hospitals and labs added as sites or entities on the same platform, with no new system to learn.
Cardiology Platform System Design FAQs
Platform system design is the structure beneath what users see. For a cardiology group, that means several entities in one database, every hospital and office set up as a site, and every charge carrying its site and component. It also means a full history of changes, role-based access and a secure cloud that scales with volume.
A separately enrolled testing facility and the physician group can run on one platform as separate entities. Each has its own tax ID, NPI, payer settings and ledger. They share the patient record, so a patient tested in the lab and seen in clinic has one chart and one balance view.
Each hospital where physicians read is set up as a site. Every professional charge from a hospital read carries that site and the professional component. Reports, edits and posting rules can then treat each hospital's work correctly, and leaders can see read volume and revenue by hospital.
Payers recoup, auditors ask what was billed and why, and corrected reports change charges after the fact. Because the database records every change instead of overwriting it, staff can show exactly how an account got to where it is. That makes audits and payer disputes faster to answer.
Data is encrypted in transit and at rest. Each user reaches only the hospitals, labs and records tied to their role, and an audit entry records each view and edit. The platform runs in a HIPAA-compliant cloud with redundant offsite backups. The platform is covered by a business associate agreement with the group.
A new office, lab or hospital is added as a site, and a new testing facility or ASC is added as an entity. Each gets its own settings while sharing tools and the patient record with the rest of the group. Staff keep working in the same system, and the new site's data appears in reports right away.
Related Cardiology Software
Platform & AI
In the revenue cycle
Platform System Design for related specialties
Sources
- 42 CFR 410.33: Independent diagnostic testing facility
- CMS National Plan and Provider Enumeration System (NPPES)
- CMS Innovation Center: Ambulatory Specialty Model (ASM)
- 45 CFR Part 164 Subpart C: HIPAA Security Standards
- 45 CFR Part 164 Subpart E: HIPAA Privacy of Individually Identifiable Health Information
GET STARTED
See Unlimited Systems in Action
Whether you're actively evaluating new technology or simply preparing for your next vendor renewal, Unlimited Systems can help you understand where your current workflows may be creating avoidable revenue risk.